How SentriaOne xSIEM Works
SentriaOne xSIEM automatically collects, normalizes, and analyzes data to identify active threats across the IT environment — from diverse, distributed log sources to raw network traffic.
Platform data flow
The diagram below shows how raw traffic and log data are ingested and processed, all the way through to actionable outcomes.
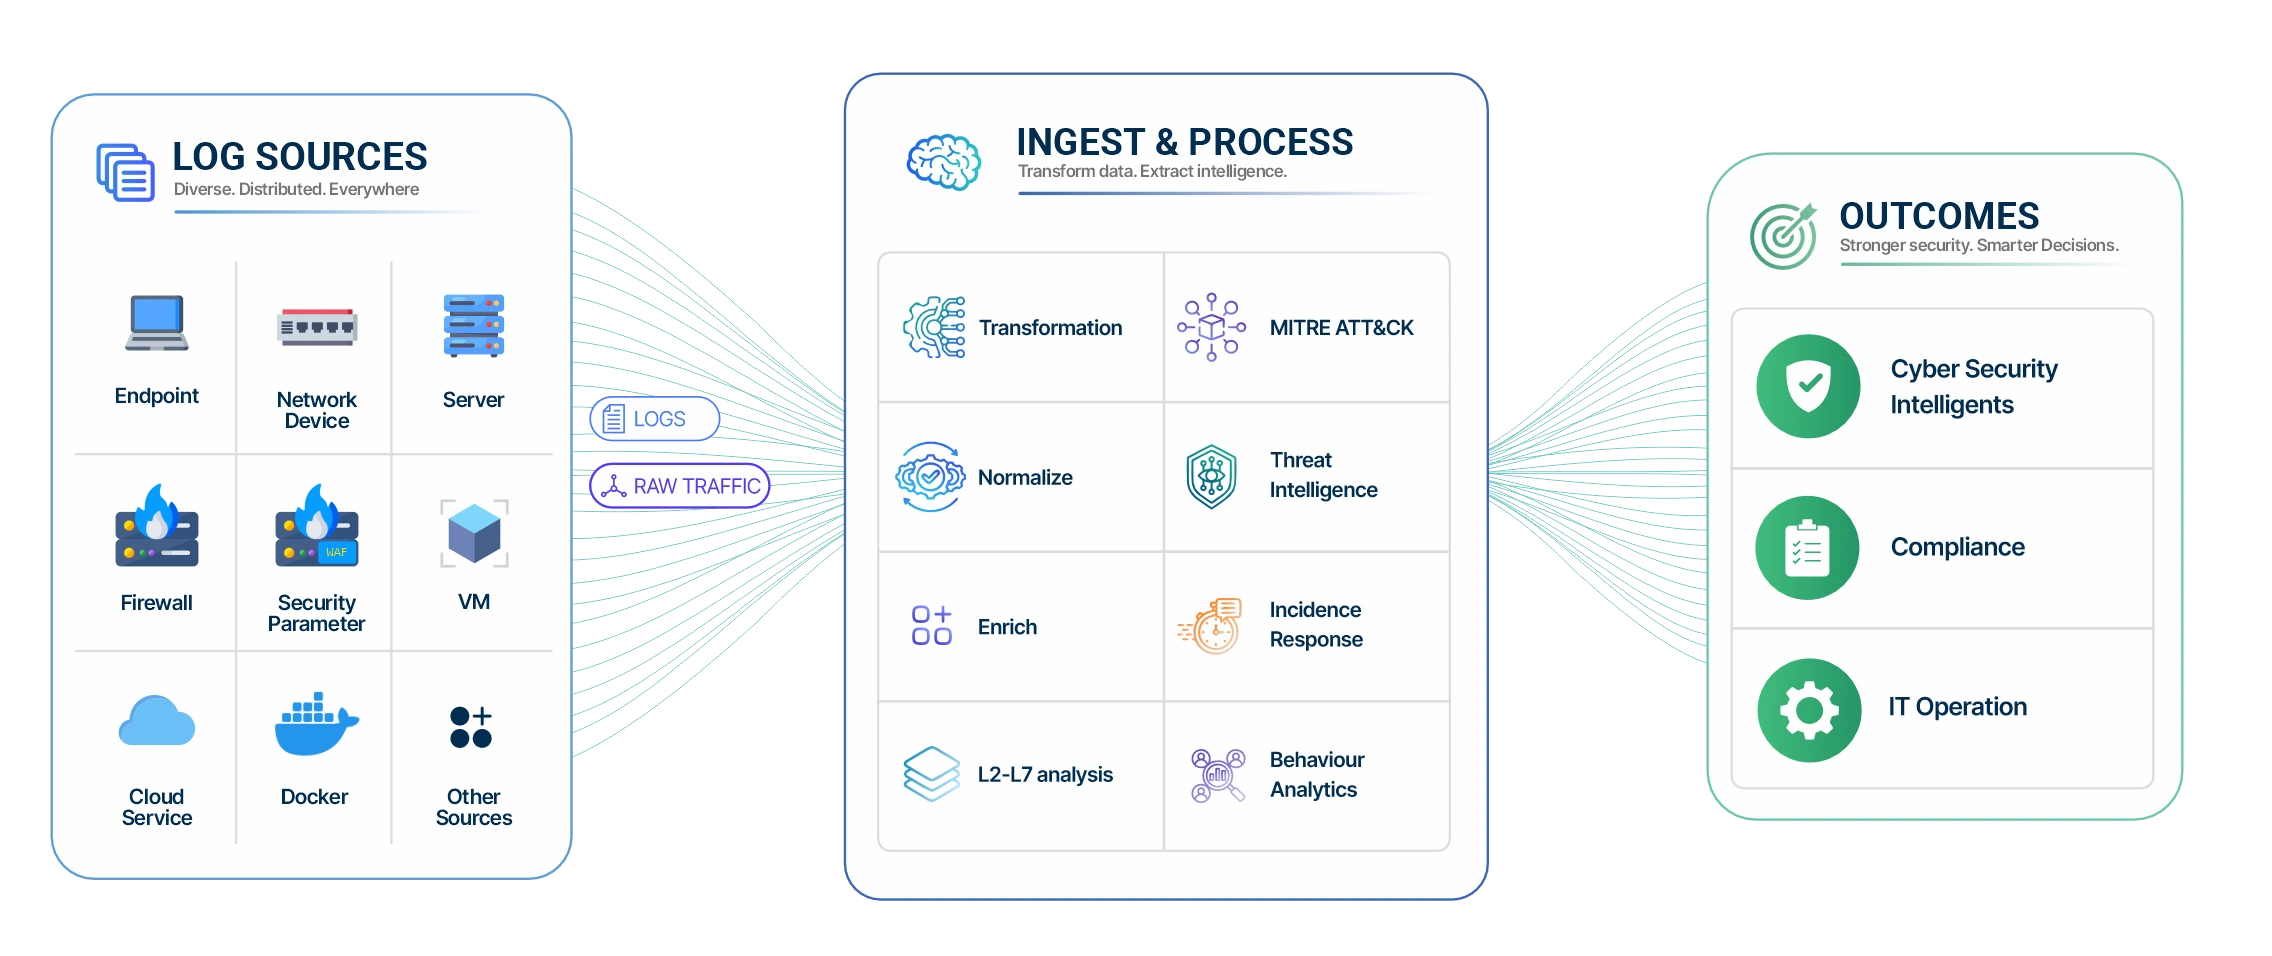
The flow consists of three stages.
1. Log sources
Data is received as logs and raw network traffic from diverse, distributed sources, such as:
- Endpoints
- Network devices
- Servers
- Firewalls
- Security perimeter devices
- Virtual machines
- Cloud services
- Docker
- Other sources
2. Ingest and process
Incoming data is transformed into intelligence through:
| Processing function | Purpose |
|---|---|
| Transformation | Converts incoming data into a usable structure |
| Normalization | Brings data from different sources into a consistent form |
| Enrichment | Adds context to the collected data |
| L2–L7 analysis | Analyzes network traffic across protocol layers |
| MITRE ATT&CK | Maps and correlates activity to the MITRE ATT&CK framework |
| Threat intelligence | Applies threat intelligence to the analyzed data |
| Behaviour analytics | Identifies anomalous behaviour |
| Incident response | Supports handling of detected incidents |
3. Outcomes
The processed data supports:
- Cyber security intelligence
- Compliance
- IT operations
Lifecycle: collect, process, detect, respond
The same flow can be summarized as a four-step lifecycle.
| Step | Description |
|---|---|
| Collect | Ingest logs and raw network traffic from endpoints, firewalls, cloud services, servers, network devices, VMs, and other sources. |
| Process | Transform, normalize, and enrich data, then store it with indexing optimized for speed and scale. |
| Detect | Identify threats using signature-based detection, ML-powered behavioural analytics, and MITRE ATT&CK correlation rules. |
| Respond | Accelerate incident response and threat hunting through a unified SOC platform. |
This page describes the platform at a conceptual level. Component-level architecture, supported source types, and configuration details are covered in the Concept, Integration, and Setting sections.