Network Classification
Menu: System › Settings › Network Classification
Network classification tells the ingest pipeline which IP ranges belong to your organization.
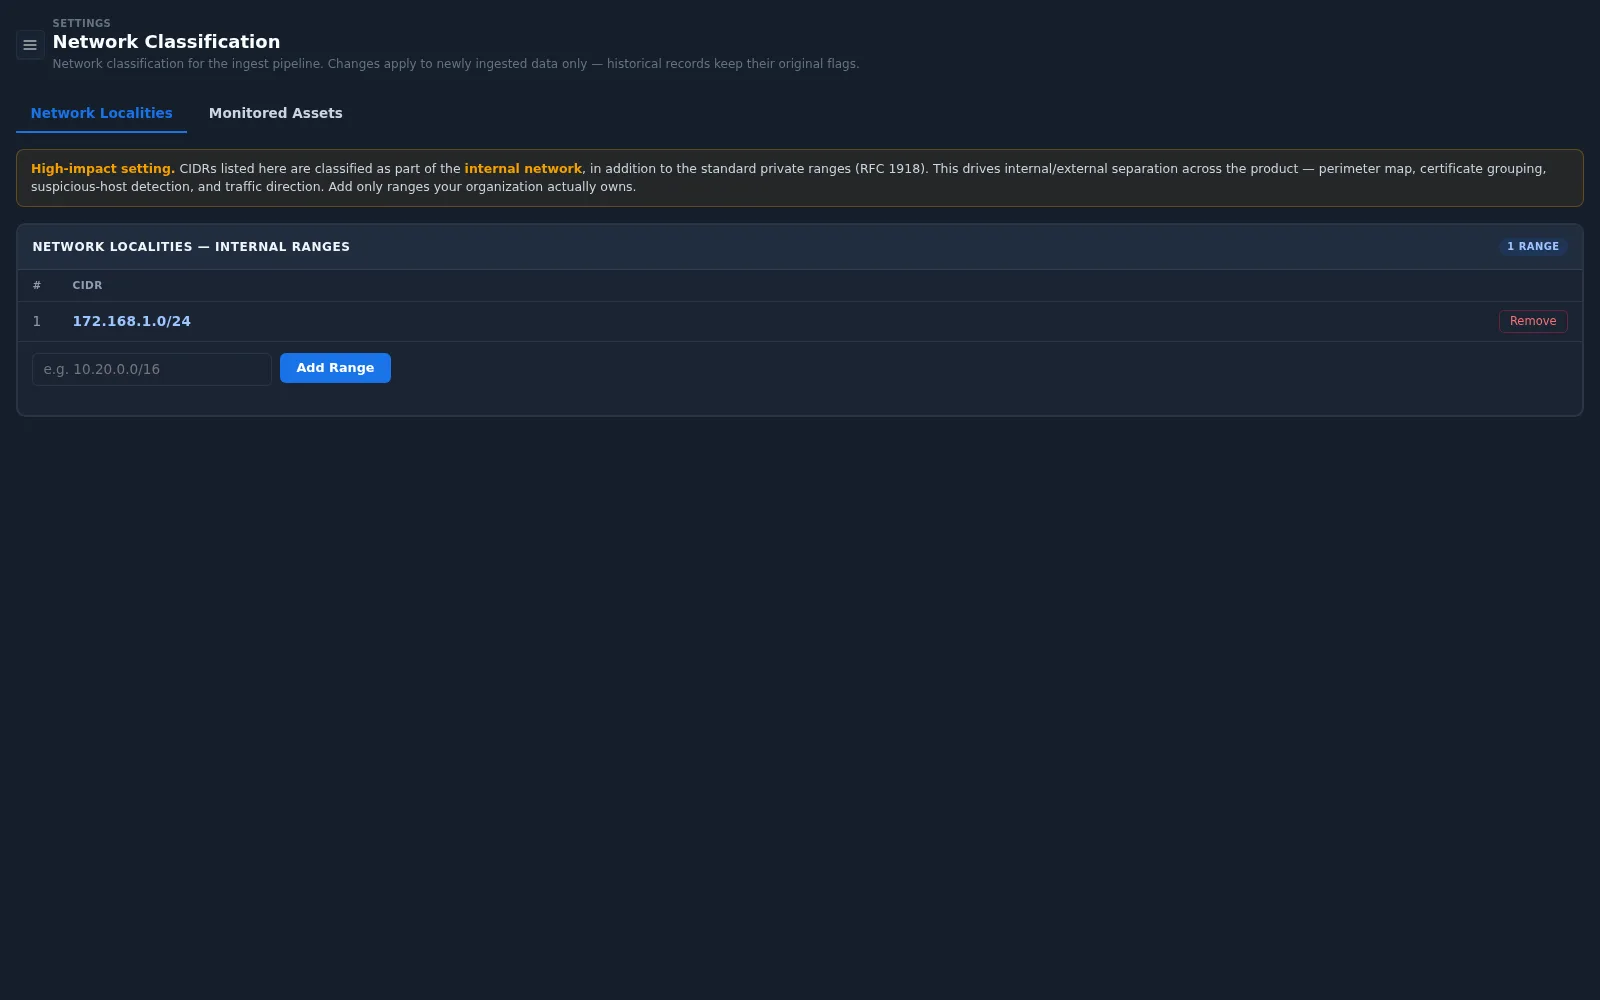
| Tab | Purpose |
|---|---|
| Network Localities | CIDR ranges classified as internal, in addition to the standard private ranges (RFC 1918) |
| Monitored Assets | Assets to be monitored |
Use Add Range to add an internal CIDR and Remove to delete one.
High-impact setting
The internal/external classification drives the perimeter map, certificate grouping, suspicious-host detection, and traffic direction across the product. Add only ranges your organization actually owns. Changes apply to newly ingested data only — existing records keep their original classification.